
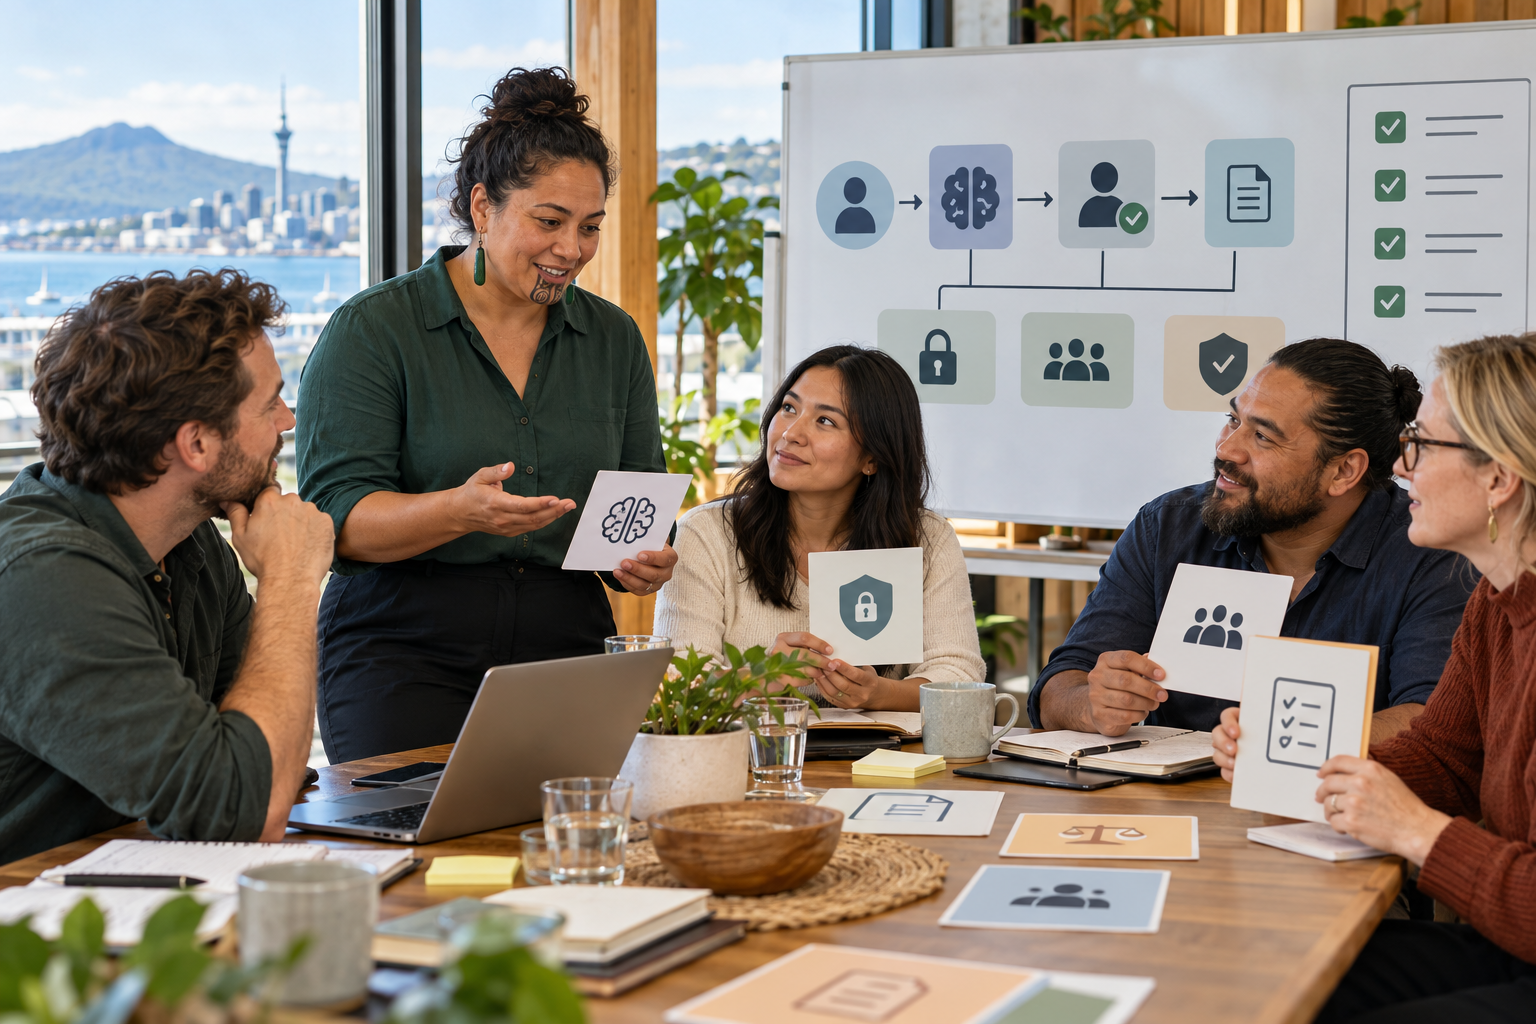
When staff use AI without a shared understanding, the business can end up with two extremes. Some people avoid useful tools because they are unsure what is allowed. Others experiment with personal accounts, confidential information or automated actions that nobody has reviewed.
An AI policy NZ small business teams can actually use does not need to be a long legal document. It needs to answer everyday questions: what can I use, what information can I enter, when must I check the result, when must I tell a customer and who can approve a higher-risk use?
A useful AI policy gives people permission to work safely, not just a list of prohibitions.
Start with the purpose of the policy
Explain why the business is introducing guidance. The purpose may be to support productivity, protect customer and staff information, maintain quality and make accountability clear. A short explanation helps staff understand that the policy is about good work, not suspicion.
State that people remain responsible for decisions and final outputs. AI can help with drafts, organisation, ideas and routine analysis, but it does not become the owner of a customer promise, financial decision, employment action or safety outcome.
Define approved, conditional and prohibited use
Use three simple categories. Approved use might include brainstorming, improving a draft, summarising public material or creating a first checklist. Conditional use might include internal information, customer messages, connected systems or content that needs a human review. Prohibited use might include entering highly sensitive information into an unapproved service, making a high-impact decision without review or presenting generated material as verified fact.
Give examples that match the work. A service team may use AI to draft a polite response, but a person must check the facts and any promise. A manager may use AI to organise a process, but should not ask it to decide which worker deserves an opportunity. A finance team may use a tool to format data, but should not accept a generated figure without checking the source.
Set a data-handling rule
Explain what information can enter an approved tool and what must stay out. Use public, internal, confidential and highly sensitive categories if those labels make sense to the business. Include names, addresses, contact details, financial records, health information, employee information, customer history, passwords and commercially sensitive plans.
Tell staff to use the minimum information needed. If a prompt only needs a paragraph rewritten, remove names and identifying details. If a document needs a structure, use a redacted or synthetic example when possible.
Explain storage and processing. Staff may not realise that a prompt or file can be retained, reviewed, processed offshore or used to improve a service. The business should approve tools with settings and controls that fit the information being used.
Keep people in the review loop
Make human review specific. The reviewer should check accuracy, completeness, tone, permissions, important dates, numbers, source material and unintended bias. The policy should say that higher-risk work needs a more experienced reviewer or a specialist.
Do not describe human review as clicking approve without reading. A reviewer needs enough context and time to question the output. If the work affects a customer, worker, price, refund, eligibility, safety matter or legal position, the person with appropriate authority should make the final decision.
Explain transparency
Customers and staff may need to know when AI is part of an interaction or decision. The policy should tell workers not to hide automated assistance when disclosure is important for trust, consent or fairness. Use simple language and offer a route to a person when someone needs clarification.
Transparency does not mean publishing every internal prompt. It means being honest about the role of AI and not making a person believe that a machine-generated answer was independently checked when it was not.
Choose a short list of approved tools
Keep an inventory of the AI tools, embedded features and connected workflows the business approves. Record the purpose, owner, data types, access model, retention settings and review date. A short list reduces shadow AI and makes it easier to update staff when a service changes.
Do not assume a feature is safe because it appears inside an existing application. Check what the feature can read, where it sends information and whether it can take actions. Add-ons and browser extensions deserve particular care because they may request broad access.
Include an incident process
Staff need to know what to do when they use the wrong tool, upload the wrong file, receive an invented answer or notice an automated action they did not expect. Tell them to stop, report quickly and preserve useful information. Avoid creating a culture where people hide mistakes until the problem becomes harder to contain.
The business should have a named contact, a simple response checklist and a way to record what happened. After the incident, review the tool, settings, training and process rather than blaming a person for every failure.
Write rules for work created with AI
Set expectations for factual checking, confidential information, copyright and the business’s own voice. Staff should not submit generated work without checking whether it contains invented claims, copied material, private information or language that misrepresents the business.
For important documents, keep a record of the source material, reviewer and final version. If the business uses AI to create an image, article, design or code, check the rights and restrictions that apply to the particular service and use.
Train with realistic scenarios
Training should be short, repeated and connected to real work. Show a safe prompt, an unsafe prompt, a plausible but wrong answer and a message that should be escalated. Practise removing personal information and checking a generated summary against the original.
Ask staff to explain the policy in their own words. If they cannot answer what data is allowed or when a human must approve, the policy is not yet practical enough. Update the examples when the tools and risks change.
Give staff a route for questions
People will encounter cases the policy does not cover. Name an owner who can answer questions and record decisions that should become future guidance. Encourage staff to ask before using a tool with sensitive data rather than relying on a guess.
Keep the route proportional to the business. A small team may need one responsible person and a shared register of decisions. A larger team may need separate owners for privacy, security, operations and quality.
Review the policy after use
Review the policy at a set interval and whenever a major tool, workflow, service or legal obligation changes. Check whether staff are using unapproved tools, whether incidents are recurring and whether the approved list still matches the work.
Measure adoption and quality. A policy that prevents every experiment may be too restrictive. A policy that allows everything without review may not protect the business. The right balance gives people a safe way to try useful ideas while keeping high-impact decisions accountable.
A plain-English policy can be strong governance
Small businesses do not need to copy an enterprise manual. They need clarity about purpose, data, tools, review, transparency, incidents and ownership. Put those points in language people will read and use. Give staff practical examples and a way to ask for help.
That is what responsible AI governance looks like in daily work. It makes good use easier, makes risky use visible and keeps the final responsibility with people who understand the customer, the business and the consequences of a mistake.
Frequently asked questions
1. Does every small business need an AI policy?
A written policy is useful whenever staff use AI for business work. It makes approved uses, data limits, review duties and reporting routes clearer.
2. What should an AI policy cover?
Cover purpose, approved tools, data handling, human review, transparency, security, incidents, quality, ownership and how the policy will be reviewed.
3. Should an AI policy ban personal accounts?
Business work should use approved accounts and tools. Explain the risk of personal or free accounts and provide a safe alternative so staff can follow the rule.
4. Can AI write customer emails without review?
It can draft them, but a person should check facts, tone, privacy, promises and any issue that could affect the customer before sending.
5. How can a small business keep the policy short?
Use plain language, three or four use categories, realistic examples and a simple escalation route. Put detailed procedures in linked internal guidance if needed.
6. How often should staff receive AI training?
Provide an introduction, refresh it when tools or risks change and use short examples during normal team meetings. Higher-risk roles may need more focused training.
7. Who should own an AI policy?
Name a person with enough authority to maintain the approved-tool list, answer questions, coordinate incident response and arrange regular review.
8. What is the safest first step for an AI policy NZ small businesses can use?
List the AI tools already in use, identify the information they handle and write simple rules for approved use, human checking and reporting mistakes.

Leave a Reply